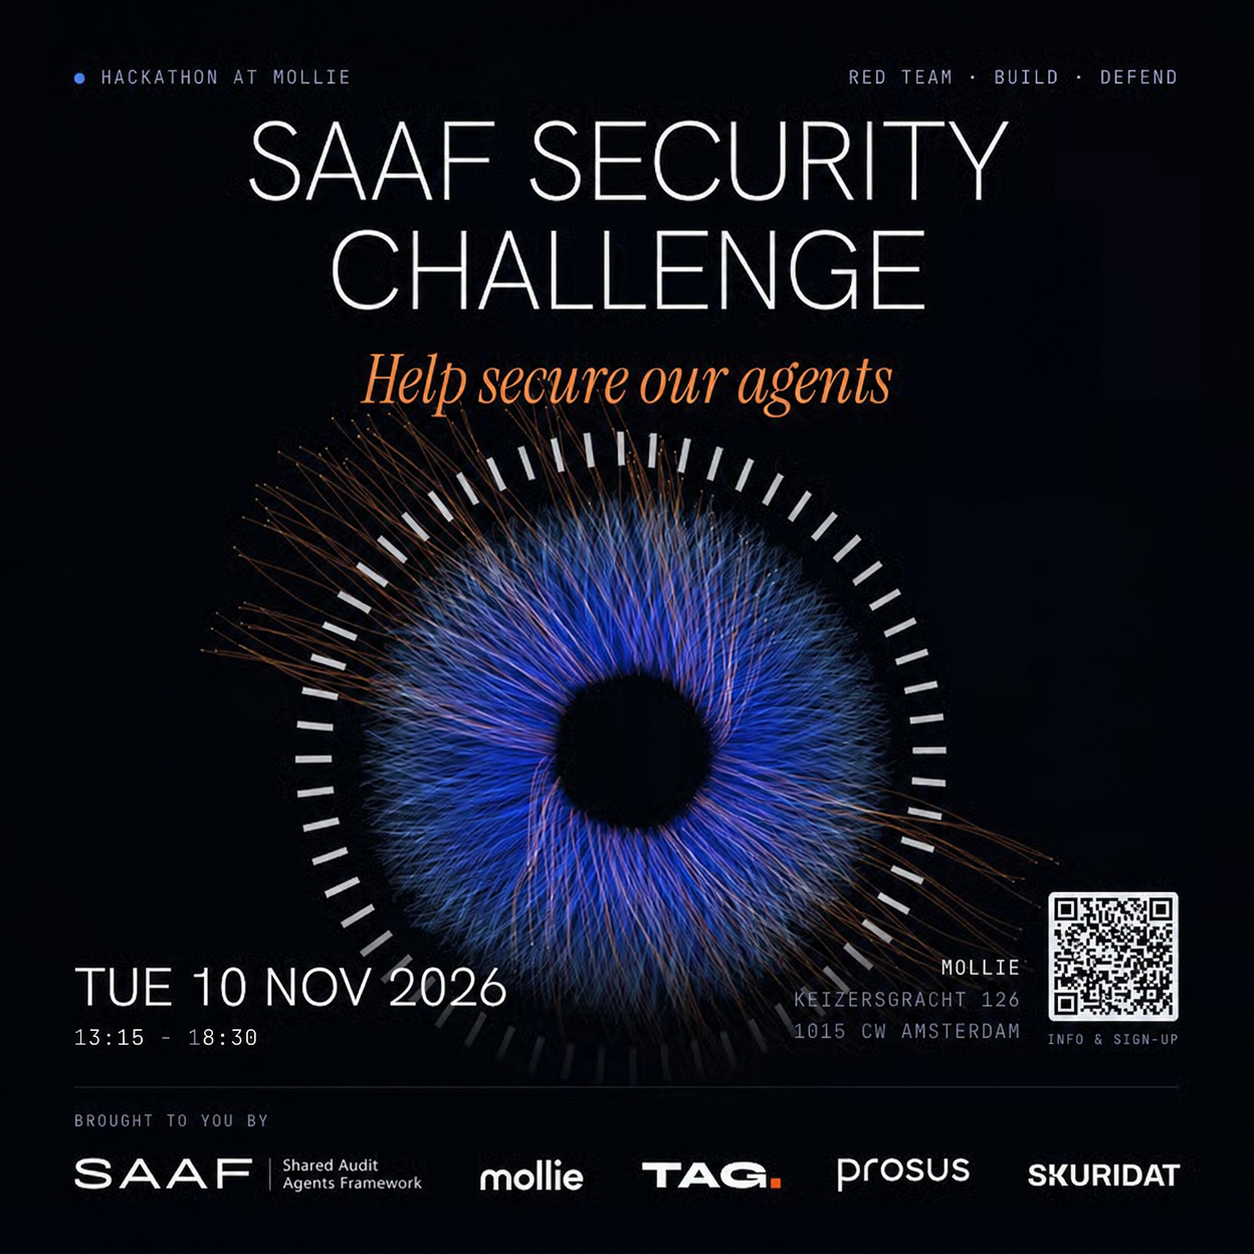
AI agents now sit inside audit, risk and compliance work. Before anyone relies on them, someone has to try to break them.
At this one-day hackathon at Mollie, red teams from Prosus and Skuridat attack the open-source agents of the Shared Audit Agents Framework (SAAF) live and show what needs fixing. Then the builders in the room build the defences, across the whole repository.
Who it's for
About 100 auditors, developers and security specialists. You don't need to be all three. Teams mix auditors who know what an agent should never do with builders who can make sure it doesn't.
The day
13:15 | Doors open, registration and coffee
13:30 | Welcome and introduction to the challenge
13:45 | Red Team: Live attacks on the agents by Prosus and Skuridat
14:25 | Lunch & Build: Teams work on hardening and securing their agents
16:45 | Team demos, results and wrap-up
17:45 | Networking drinks
18:30 | Close
Brought to you by
SAAF · Mollie · TAG · Prosus · Skuridat
About SAAF
The Shared Audit Agents Framework is an open framework for auditing, testing and hardening AI agents in audit and compliance. It's built in hackathons by auditors, engineers and ethical hackers, and has ties to NOREA, ISACA, the IIA and NBA.
More info: https://saafproject.com
About TAG
TAG stands for To Achieve Greatness. It's a community of builders, hackers and creators in Amsterdam. Not desks and WiFi: a house where people ship every month, show what they built, and do it again. For this challenge TAG brings its builders to Mollie, so the room is a mix of auditors and developers.
More info: www.tag.space/upcoming/saaf-security-challenge
Please register so we can check you in at the door. The address is shared once you're approved.
By registering you agree to how we handle your data: tag.space/privacy
 Tijs Nieuwboer
 Mathijs Schouten
 Sofia Frumkina